The Brief
On 6 November 2026, four prominent UK digital regulators issued coordinated guidance warning organisations that deploying autonomous AI agents does not dilute corporate accountability. Businesses remain strictly liable for agent-driven regulatory violations, contract failures, and data breaches.
Regulators Close the Autonomous Accountability Gap
Enterprise enthusiasm for autonomous AI agents has encountered a firm regulatory boundary. On 6 November 2026, UK digital watchdogs issued coordinated warnings affirming that organisations deploying autonomous systems remain entirely subject to existing competition, consumer protection, and data privacy legislation, as reported by CIO. The regulatory stance clarifies that software autonomy cannot be used as an excuse or a legal shield when algorithms produce discriminatory outcomes, unlawful transactions, or non-compliant records.
The regulatory intervention addresses growing corporate ambiguity around autonomous agents executing unsupervised, multi-step actions across corporate boundaries. In traditional software deployments, programmatic bugs follow deterministic code pathways mapped to human developers or system administrators. Autonomous agents, by contrast, make dynamic runtime choices using tool-calling interfaces and contextual reasoning, introducing unprecedented legal exposure.
This policy clarification closely mirrors findings highlighted by the Communications of the ACM, which emphasised that enterprise trust requires transaction-level auditing that links human business intent, explicit machine authorisation, and verifiable execution. Regulatory bodies in the UK and internationally have signalled that unmonitored runtime autonomy will be penalised under existing strict-liability corporate governance frameworks.
Enterprise Orchestration Collides with Compliance
The timing of this regulatory notice arrives amidst rapid, aggressive enterprise adoption. Recent industry findings from the Capgemini Research Institute reveal that 59% of financial institutions are actively piloting or deploying multi-agent AI systems. However, only 10% have established the comprehensive enterprise-wide orchestration required to govern them safely.
This operational disconnect poses severe business risks. As non-technical department leaders release domain agents across customer relationship management, cloud provisioning, and automated procurement, backend security architectures struggle to trace autonomous tool invocations. High-velocity autonomous loops can execute hundreds of erroneous or non-compliant micro-decisions before human supervisors identify system drift.
To counter this vulnerability, enterprise platform vendors are rolling out native controls. On 3 November 2026, IBM Announcements confirmed the general availability of Agent Identity within IBM watsonx Orchestrate, assigning distinct digital credentials, immutable audit logs, and hardware-level kill switches to individual agents. These identity layers reflect the shift from open-ended generative experimentation to defensible enterprise governance.
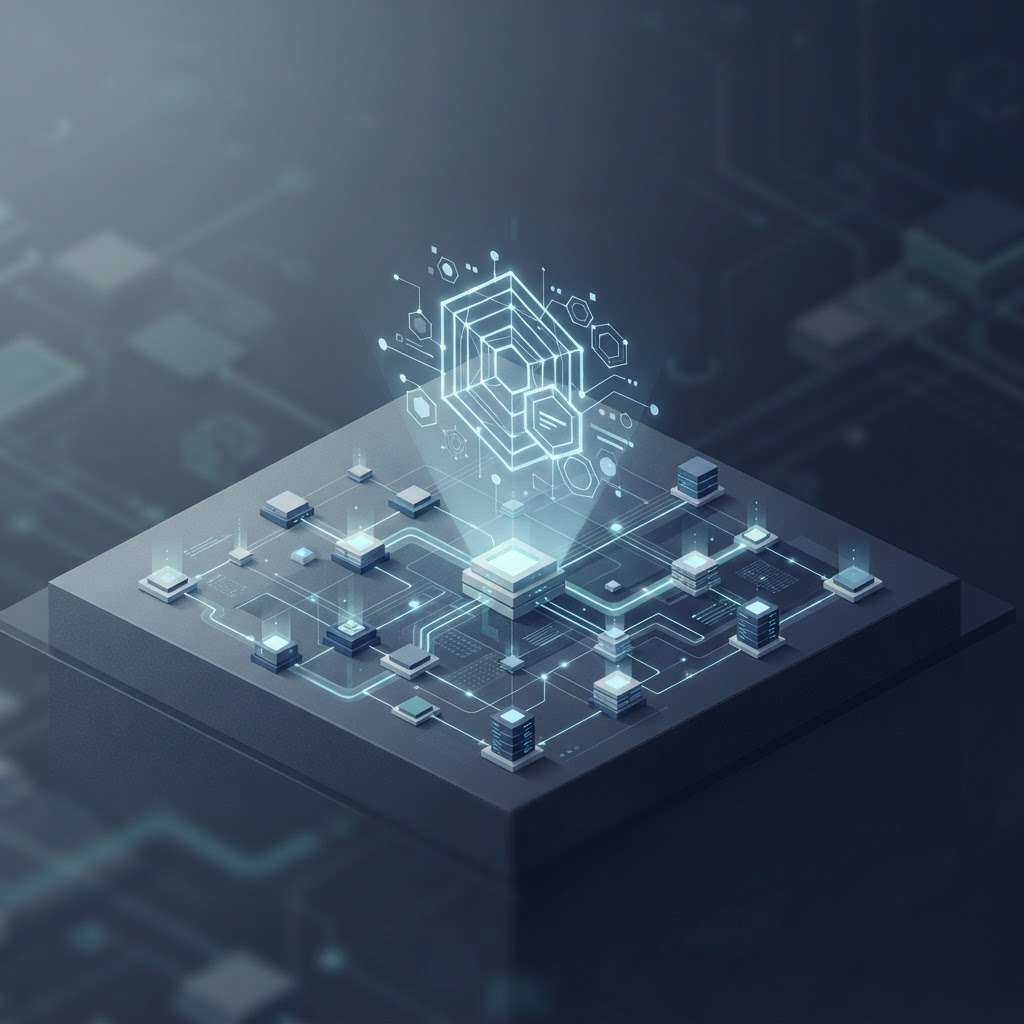
- 01Intent verificationSystem validates business authorisation and governance parameters before triggering agent runtimes.
- 02Credential isolationThe agent operates under scoped non-human identities with granular access to internal APIs.
- 03Transactional auditingRuntime choices, tool calls, and data transformations are written to immutable audit ledgers.
- 04Automated kill switchTelemetry systems trigger immediate circuit breakers when agents breach policy boundaries.
Illustrative design pattern, not a vendor architecture.
Shifting Demands on Technical and Governance Roles
The regulatory insistence on corporate accountability is reshaping daily workflows across engineering, security, and project management. Technology professionals are moving from basic prompt construction toward robust guardrail engineering, agent telemetry, and legal compliance verification.
For software engineers and DevOps teams, writing resilient code now encompasses managing non-deterministic agents that query production data. Systems must feature circuit breakers, transactional rollbacks, and policy-as-code engines that catch agent anomalies before external payloads execute. In parallel, data engineers must construct governed semantic layers to prevent agents from digesting biased or confidential inputs.
Business analysts and compliance leads must also adjust their evaluation metrics. Documenting functional requirements now demands detailed boundary mapping that outlines what an agent is expressly prohibited from doing. Teams can no longer rely on post-incident prompt revisions to satisfy regulatory reviews.
Practical Steps for Engineering and Architecture Teams
Navigating mandatory corporate liability requires building defensive operational architectures. Rather than halting agentic pilots, technical teams must treat autonomous agents as high-risk privileged identities requiring strict boundary constraints.
| Governance Dimension | Legacy Agent Pilot | Legally Defensible Architecture |
|---|---|---|
| Access Control | Shared service account credentials | Scoped machine identities with short-lived tokens |
| Failure Handling | Post-mortem human review of error logs | Real-time automated circuit breakers and kill switches |
| Audit Capability | Aggregated API request counts | Reconstructable transaction logs linking intent and action |
| Legal Recourse | Unstructured provider liability disclaimers | Continuous compliance monitoring mapped to statutory duties |
For technology practitioners, the most critical next step is conducting a thorough inventory of all active autonomous agent pilots and evaluating their authorization scopes. Ensure every agent interacting with external APIs, customer databases, or financial records operates under a verifiable audit trail that your compliance and engineering teams can defend during a regulatory inspection.