The Brief
AI agents need more than a clever prompt. Reliable systems save progress, pause for consequential decisions and leave a usable record of what happened. For learners, that makes integration, testing and security valuable companions to generative AI skills.
The Signal: A Successful Action Can Still Be Wrong
An agent issues a customer credit. The request succeeds. The service stays online. But who authorised the payment?
That is the question at the centre of Richard Ewing’s 21 September CIO opinion article. He describes an architecture review in which a technically successful refund lacked a clear business-authorisation trail. It is an illustrative account, not a measurement of how often agents fail, but the distinction matters: a working system is not necessarily an authorised system.
For teams building agents that work across several steps, this is a useful shift in emphasis. The question is no longer just whether a model can produce a good answer. It is whether the surrounding software can control what happens next.
Beyond Chat Does Not Mean Beyond Supervision
A conversational interface can use tools and remember context. An agent can still require supervision. The useful distinction is the responsibility delegated to the system, not whether it has a chat window.
Consider a supplier-review assistant. It reads documents, checks missing information and prepares a recommendation. Those steps may be low risk. Changing a supplier’s payment details is different: it needs stronger checks and a clearly accountable decision-maker.
The Agents SDK human-in-the-loop documentation describes a concrete implementation pattern: sensitive tool calls can interrupt execution, a person can approve or reject them, and a serialised run state allows work to resume. This is a documented capability, not proof that a particular deployment is safe.
Our analysis: useful autonomy is bounded autonomy. Automate routine work where the consequences are understood. Escalate consequential actions with enough evidence for a person to make a meaningful decision.
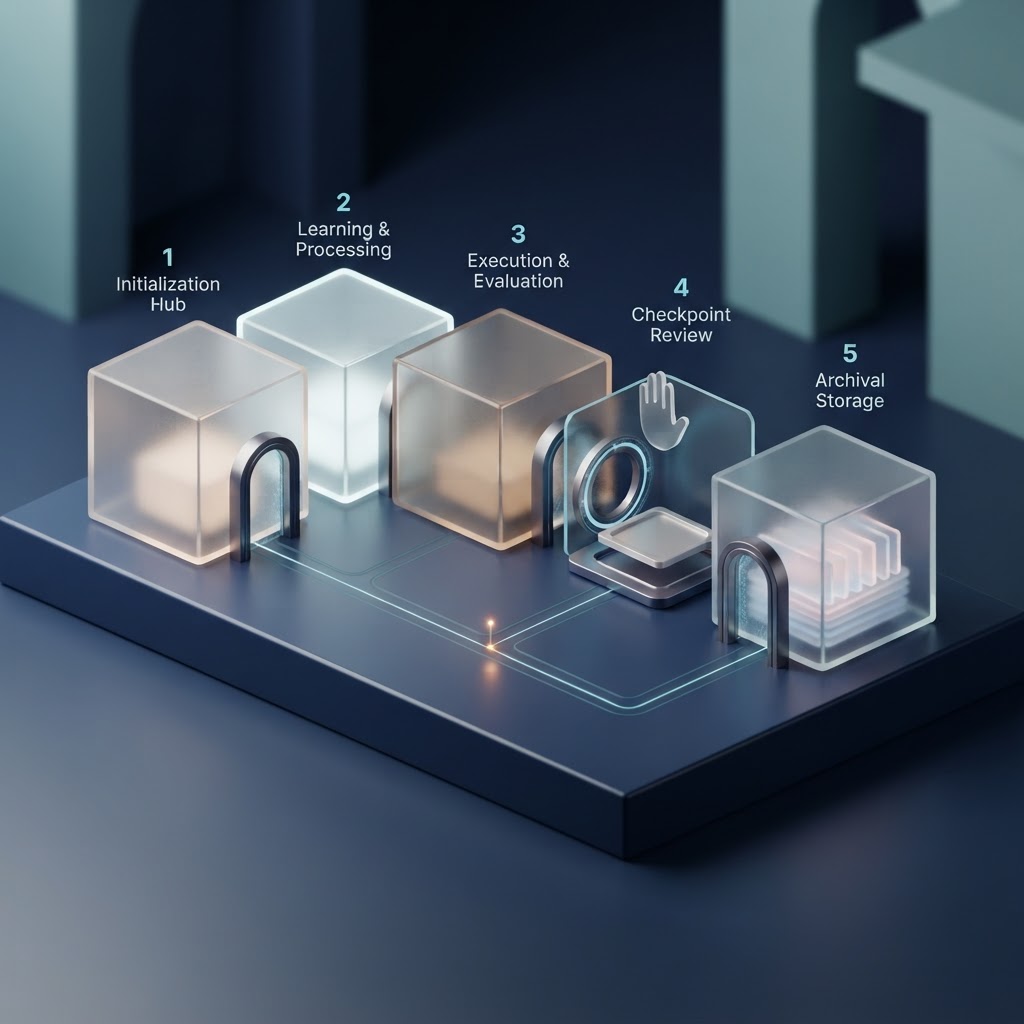
- 01DefineSet the goal, limits and owner.
- 02InspectGather evidence using scoped tools.
- 03SaveCheckpoint progress before a pause.
- 04ApproveReview consequential actions.
- 05RecordLog the outcome and any recovery.
Illustrative design pattern, not a vendor architecture.
The Hidden Skill: Recovering Without Repeating
Long-running work is rarely one uninterrupted model response. An external service times out. An employee reviews a request tomorrow. A server restarts. The application must know where it stopped.
LangGraph’s persistence documentation distinguishes checkpoints for a particular thread from stores for information shared across threads. It also warns that in-memory checkpoints do not survive a process restart. Remembering a conversation and reliably recovering a workflow are related, but they are not interchangeable.
Recovery introduces another engineering problem: retries. If a payment succeeds but its acknowledgement is lost, repeating the request can create a duplicate. Our recommendation is to use idempotency keys where supported, record operation outcomes and test ambiguous failures rather than assuming every retry is harmless.
Connectivity Is Not Permission
Connecting an agent to more systems increases its usefulness and the consequences of a mistake. Model Context Protocol provides a standard interface for integrations, but adopting it does not remove the need for an application’s own security controls.
The MCP draft security guidance discusses risks including confused-deputy attacks in proxy authorisation flows. Its recommended protections include explicit per-client consent and strict redirect validation. These are specific implementation concerns, not a claim that every MCP connection is vulnerable.
For a practical agent project, separate what a tool can do from what this run is permitted to do. Give the agent only the access it needs, validate inputs outside the model and treat text retrieved from documents as evidence, not as permission to change the workflow.
What This Means for Your Training
These capabilities do not establish a forecast for hiring or guarantee a job. They do offer concrete ways to make a portfolio more credible across Pathway AI’s training areas.
| Training Area | A Useful Skill to Demonstrate |
|---|---|
| AI Agents & Generative AI | Define tool boundaries and evaluate outcomes, not just fluent responses. |
| Salesforce | Design an approval path before an assistant changes a consequential CRM record. |
| Cloud & DevOps | Recover from a restart, trace failures and enforce execution budgets. |
| Cybersecurity | Test permission boundaries and untrusted document inputs. |
| Data & Analytics | Check provenance, validate fields and expose missing evidence. |
| Software Engineering | Make retries safe and test failure paths alongside successful ones. |
Your Next Build: A Small Agent With Real Controls
Build a supplier-review assistant using fictional records. Keep the scope deliberately small: read evidence, identify gaps and draft a recommendation. Do not connect it to live payments or customer data.
- Set the boundary. Write down which actions are allowed, which require approval and which are forbidden.
- Make it pause. Show the reviewer the proposed change, supporting evidence and relevant policy before approval.
- Break it deliberately. Restart the application mid-task and simulate a timed-out write. Demonstrate recovery without a duplicate action.
- Show the evidence. Include a short trace, your tests and the limitations in your portfolio.
The Takeaway
A stronger agent demo is not one that claims unlimited independence. It is one that shows precisely when the system acts, when it stops and how a person can understand the result.