The Brief: ISC2 has launched a vendor-neutral Cyber-AI Workforce Coalition alongside plans for its inaugural AI security certification in early 2027. The move establishes formal role definitions and defensive competencies as agentic automation reshapes traditional cyber careers.
On 27 October 2026, cybersecurity certification body ISC2 announced the formation of the Cyber-AI Workforce Coalition, an initiative designed to establish vendor-neutral standards for security professions impacted by artificial intelligence. Operating as an industry convener, the coalition aims to clarify emerging competencies, update role definitions, and support career changers and practitioners as automated workloads alter day-to-day enterprise defence.
Alongside the coalition rollout, ISC2 revealed that its first formal AI security certification is scheduled for general availability in early 2027, backed by a 3,000-volunteer pilot testing phase. The twin announcements highlight an acute industry pivot: security operations centres (SOCs) are moving beyond conceptual governance to deploy concrete architectural controls over autonomous, agentic tools.
The Shift from Manual Triage to Agent Supervision
The necessity for standardised AI security training comes amid rapid automation within enterprise security teams. Industry research from Andreessen Horowitz on the new security agenda highlights that 87% of security organisations anticipate rising cybersecurity spending, driven directly by AI-enabled threats and the tooling required to secure internal agents. SOC automation, offensive security, and internal agent protection are absorbing the largest share of fresh capital allocations.
At the same time, traditional tier-one triage roles are disappearing as natural-language orchestration handles log aggregation, initial alert triage, and correlation. Rather than parsing static logs manually, junior and mid-level analysts must now validate agent reasoning, audit prompt and tool calls, and manage automated remediation actions across heterogeneous corporate environments.
Closing the Governance and Network Visibility Gap
Securing machine-to-machine interactions has become urgent as developers deploy autonomous agents with active API access. On 26 October 2026, network security firm Fortinet launched its FortiGuard Inline AI Security Service, incorporating context-aware guardrails that assess tool-calling protocols such as Anthropic's Model Context Protocol (MCP) and inspect live application traffic before actions execute.
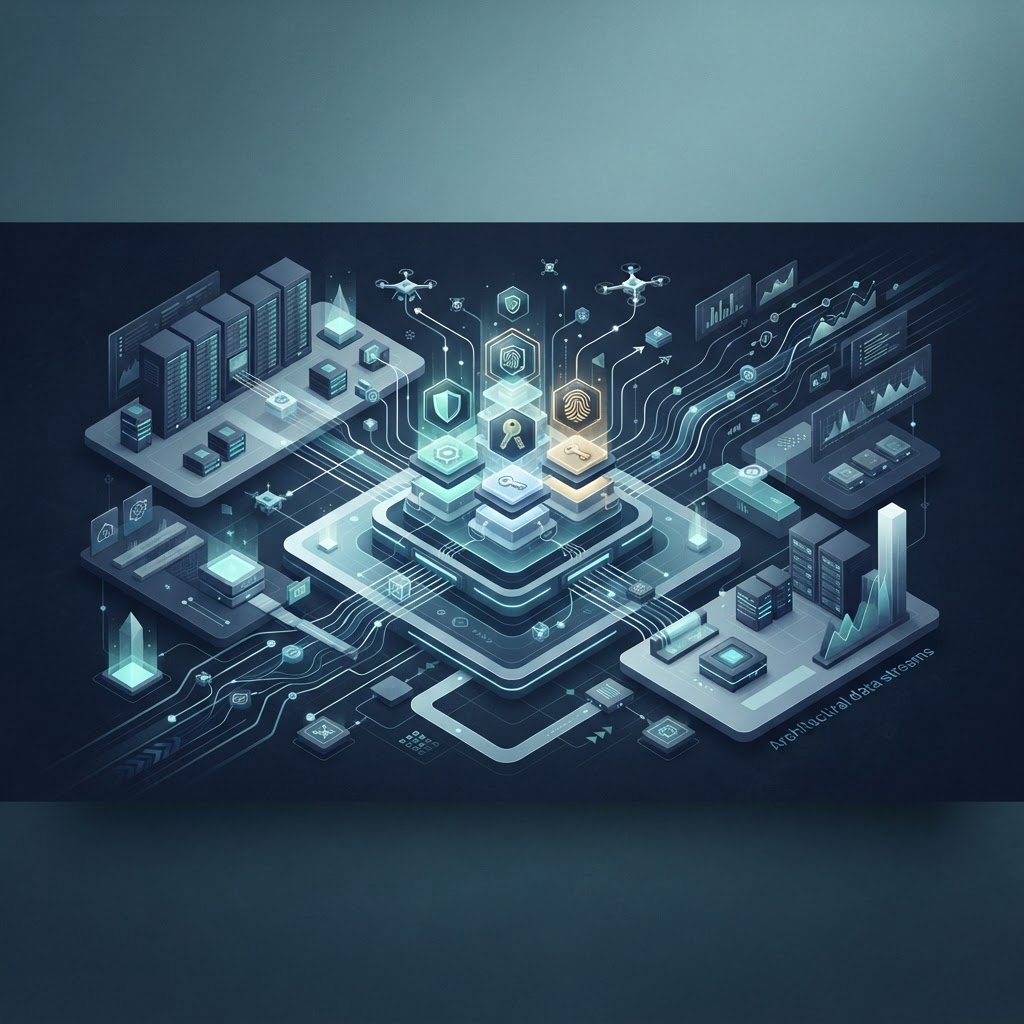
- 01Discover Unmanaged AssetsIntercept DNS and API requests to locate rogue tools and shadow autonomous agents.
- 02Enforce Protocol GuardrailsInspect runtime application prompts, model outputs, and MCP tool invocations in line.
- 03Audit Runtime PrivilegesIsolate agent identities using least-privilege tokens and verify reasoning traces.
- 04Review Defensive TelemetryIngest agent execution metrics into the SOC to train human operators on incident oversight.
Illustrative design pattern, not a vendor architecture.
Traditional endpoint detection and response (EDR) platforms inspect IP addresses and file hashes, but they cannot evaluate semantic risk or unintended multi-step tool executions. ISC2's curriculum prioritises these gaps, ensuring practitioners learn how to audit agentic behaviour alongside standard network controls.
Workforce Implications Across Core Disciplines
The restructuring of defensive cyber roles extends across the technology ecosystem. For cloud engineers and DevOps specialists, autonomous pipelines demand automated secrets rotation, short-lived machine tokens, and continuous policy-as-code testing.
| Discipline | Traditional Cyber Focus | Emerging Cyber-AI Focus |
|---|---|---|
| SOC Operations | Manual log parsing and alert disposition | Reasoning validation and agent policy tuning |
| Cloud Architecture | Static role-based access control (RBAC) | Ephemeral credentials for autonomous agent runtime |
| Application Security | Static code analysis and input sanitisation | MCP tool-call auditing and prompt injection defence |
| Governance & Compliance | Annual policy audits and compliance checklists | Real-time AI agent telemetry and algorithmic oversight |
For business analysts and data specialists, understanding the provenance of data feeding internal language models is now a primary defensive priority. Security is no longer confined to the IT perimeter; it requires validating data pipelines against poison vectors, pipeline exfiltration, and unauthorised model context sharing.
Practical Pathways for Technology Professionals
For students and career changers preparing to enter defensive technology, the emergence of formal credentials offers clear navigational markers. Rather than focusing exclusively on legacy vulnerability scanning techniques, candidates should align their development with system-level AI oversight.
A realistic immediate next step is to explore participation in open AI security frameworks and pilot certifications, such as the upcoming ISC2 validation cohorts. Gaining hands-on familiarity with agent communication standards, proxying LLM API endpoints, and evaluating multi-step automated workflows will differentiate technical professionals across all security specialisations over the coming year.