The Brief: Cloud platform teams are transitioning from retrofitted spending dashboards to automated governance, driven by native hyperscaler tools designed to cap unpredictable AI inference and training costs.
Controlling infrastructure expenditure across enterprise estates has reached an operational pivot point. Mid-September 2026 brought a significant product expansion as Google Cloud introduced native FinOps tools for AI cost control, addressing the escalating financial volatility of generative model orchestration and compute consumption. This release responds directly to rising organizational demand for granular, real-time budget guardrails surrounding high-capacity GPU clusters, API-based foundation models, and vector processing pipelines.
While hyperscalers have historically treated infrastructure billing as an asynchronous accounting exercise, modern workloads render monthly reviews ineffective. Runaway autonomous agent loops or unoptimised inference calls can deplete monthly budgets in hours rather than weeks. The rollout marks a concerted transition across public cloud infrastructure, positioning financial engineering directly within automated developer delivery pipelines.
The Shift to Preventative AI Cost Guardrails
Traditional cloud financial operations focused on right-sizing virtual machines and claiming reserved instance discounts. The rapid enterprise adoption of large foundation models, such as Gemini on Vertex AI or rival hosted models, introduced dynamic pricing variables that bypass conventional monitoring tools. These variables include context-window token size, persistent cache allocations, and specialized accelerator reservations.
The new capability suite provides platform teams with predictive thresholds, active telemetry hooks, and policy-driven operational gates. Rather than relying on downstream invoice reconciliation, engineering leads can enforce deterministic budgetary limits directly across shared Kubernetes workloads and managed model APIs.
Automated Governance Inside Platform Engineering
Internal developer platforms are increasingly adopting preventative guardrails by design. According to platform strategy insights from Growin's 2026 platform engineering review, mature engineering organisations are prioritising embedded platform governance over manual management approvals. Systems that embed compliance, security, and cost boundaries directly into automated developer self-service workflows significantly curb accidental architectural sprawl.
This operational shift requires platform engineers to build preventative landing zones that incorporate financial controls alongside role-based access control. As detailed by PlatformEngineering.org's predictions for 2026, mature platforms are making pre-deployment cost gates a foundational requirement, establishing explicit token budgets to govern agentic workloads and multi-model clusters before pipelines deploy.
Operationalising Cloud Cost Controls
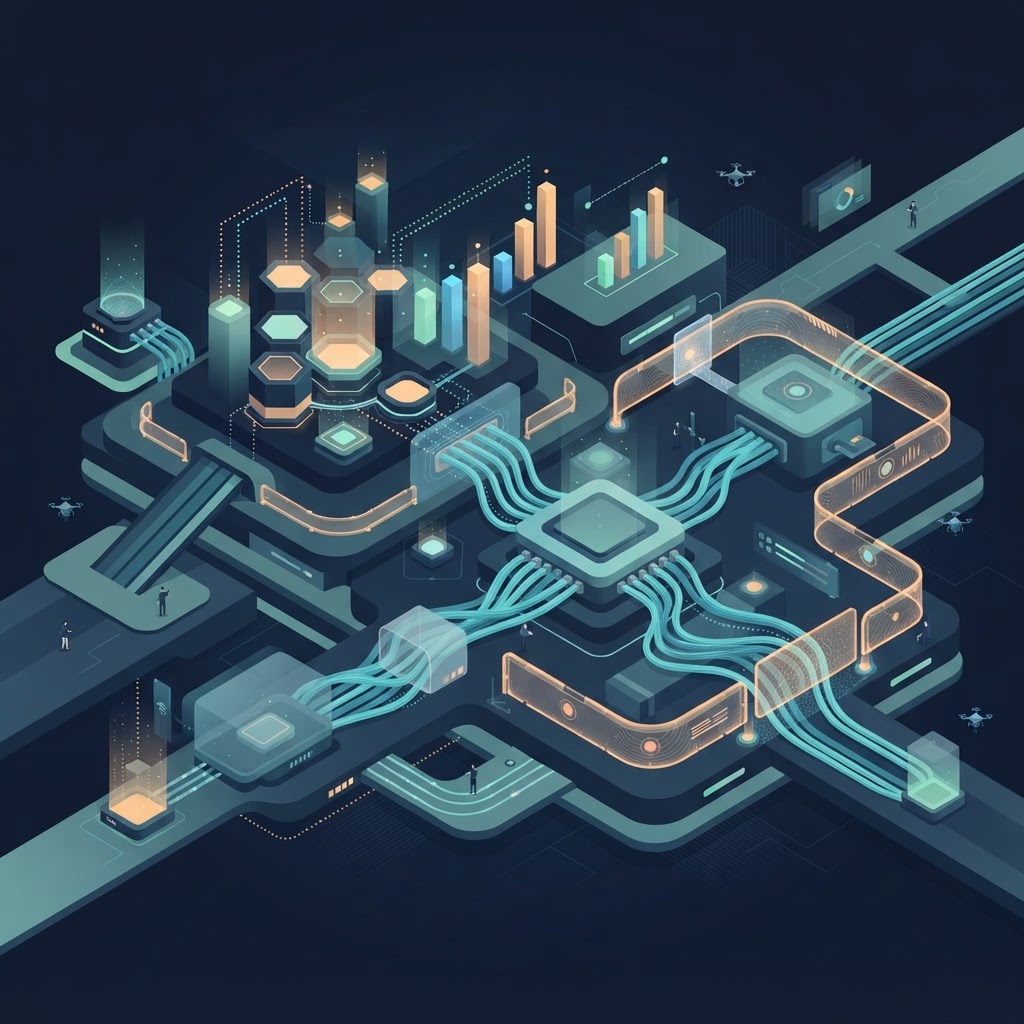
Implementing automated financial guardrails across cloud estates requires tight coordination between infrastructure teams and software delivery channels. Cloud architects are turning to standardised execution flows to integrate real-time budget telemetry into continuous integration pipelines.
- 01Inventory workloadsCatalog GPU allocations, API endpoints, and model dependencies
- 02Establish unit economicsMap token consumption thresholds to specific business features
- 03Define IaC policy gatesEmbed financial guardrail policies into pre-deployment pipelines
- 04Activate telemetry hooksConnect automated circuit breakers to real-time spend anomalies
Illustrative design pattern, not a vendor architecture.
Multicloud Complexity and Technical Portability
Modern cloud operations rarely exist in isolation. Multi-cloud adoption remains dominant across enterprises seeking to avoid vendor lock-in, with industry analysis from Qovery on cloud migration dynamics stressing that workflow lock-in inside proprietary developer portals represents the single greatest long-term cost obstacle. Teams relying on proprietary vendor mechanisms must ensure policy logic remains portable across environments like AWS Bedrock and Microsoft Azure.
Platform teams balancing mixed workloads can evaluate how operational responsibilities are shifting across standard cloud tiers:
| Operational Dimension | Traditional FinOps Approach | Preventative AI Platform Model |
|---|---|---|
| Cost Visibility | Post-billing monthly reporting | Real-time token and compute telemetry |
| Policy Enforcement | Manual managerial approval gates | Automated pre-merge Infrastructure as Code tests |
| Workload Governance | Idle server deallocation | Dynamic circuit breakers on inference APIs |
| Cross-Cloud Portability | Vendor-specific billing portals | Open API metadata standards across clusters |
Career Implications and Strategic Next Steps
For career changers, cloud architects, and platform practitioners, these developments redefine core competency expectations. Understanding cloud provisioning syntax alone is no longer sufficient. Modern cloud engineering demands fluency in telemetry data pipelines, automated policy enforcement, and infrastructure unit economics.
Professionals seeking to future-proof their skill sets should audit their current infrastructure configurations. A pragmatic next step is to introduce pre-commit cost-linting checks on existing Terraform or Pulumi configurations, defining explicit spend limits before generative AI application instances reach production environments.