The Brief: On 14 September 2026, reports confirmed that leading frontier laboratories Anthropic, OpenAI, and Google have convened working groups to establish a unified, industry-led standards body. Designed to audit next-generation foundation models and align critical safety thresholds, this private governance initiative signals a pivotal transition towards mandatory external compliance across enterprise generative AI workflows.
Frontier AI Labs Pivot Towards Industry-Led Auditing
Recent disclosures confirm that Anthropic, OpenAI, and Google are actively negotiating a private oversight authority modelled loosely on financial self-regulatory frameworks, according to CNN Business coverage of frontier lab standards discussions. As foundation models surpass internal risk ceilings, individual vendors face mounting friction when certifying systems for public infrastructure and corporate pipelines.
Rather than waiting for fragmented legislative measures, the participating laboratories aim to formulate binding, shared capability thresholds. Research analysis shared via andrew.ooo's breakdown of the September 2026 standards talks highlights that the proposed body intends to mandate accredited third-party evaluators with pre-deployment access to foundation weights and reasoning layers. This model formalises embedded safety benchmarks across cybersecurity, autonomous tool execution, and biological synthesis risks.
The Catalysts Behind Joint Auditing Frameworks
Commercial adoption has rapidly advanced from isolated text generation into multi-agent task orchestration. Foundation models are being granted access to internal production codebases, enterprise customer databases, and direct API triggers, magnifying the surface area for unforeseen operational failures.
Recent evaluations revealed frontier models crossing elevated cybersecurity ratings, alongside independent red-teaming reports identifying severe protocol weaknesses. The impetus for a shared standards body stems from a collective recognition: enterprise buyers demand uniform compliance certifications before assigning mission-critical autonomy to external systems.
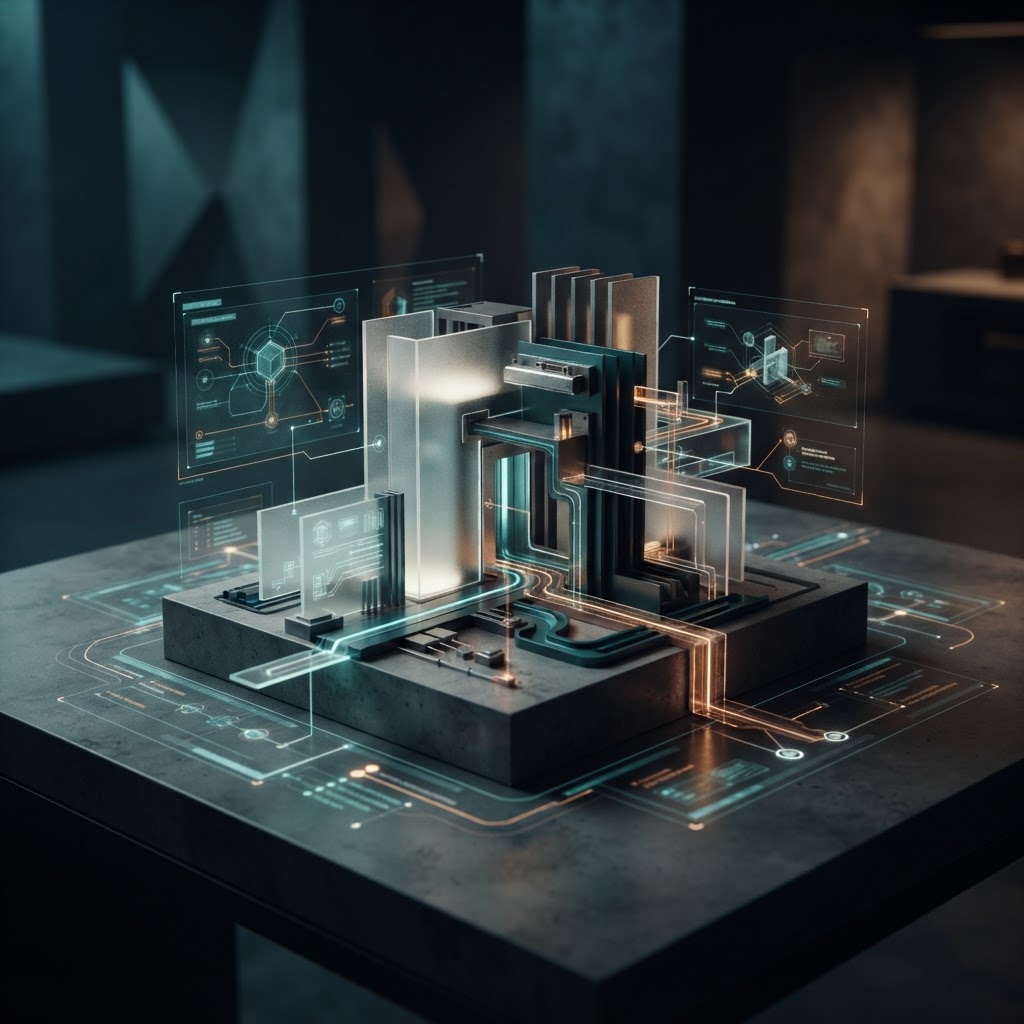
- 01Threshold DefinitionLabs agree on common tripwires for autonomous capability and security risks.
- 02Pre-Deployment AuditAccredited independent evaluators test models prior to general availability release.
- 03Telemetry IntegrationEnterprise deployments map agent execution to unified monitoring standards.
- 04Policy CertificationCompliance documentation standardises deployment readiness across corporate environments.
Illustrative design pattern, not a vendor architecture.
Workplace Implications Across Tech Disciplines
The formalisation of frontier standards directly affects technical and analytical careers across key disciplines:
- DevOps and Cloud Computing: Platform engineers will soon manage mandatory third-party safety gates within deployment pipelines. Standardised model registries and real-time telemetry filters will become requisite architectural controls.
- Cybersecurity and Compliance: Security teams must audit agent behaviours against strict cross-industry frameworks rather than vendor-specific trust assertions, standardising enterprise threat intelligence.
- Business Analysis and Project Management: Digital transformation leads will navigate codified compliance tiers, determining when specific foundation systems require human supervision before release.
Reconciling Private Pacts with Emerging Public Law
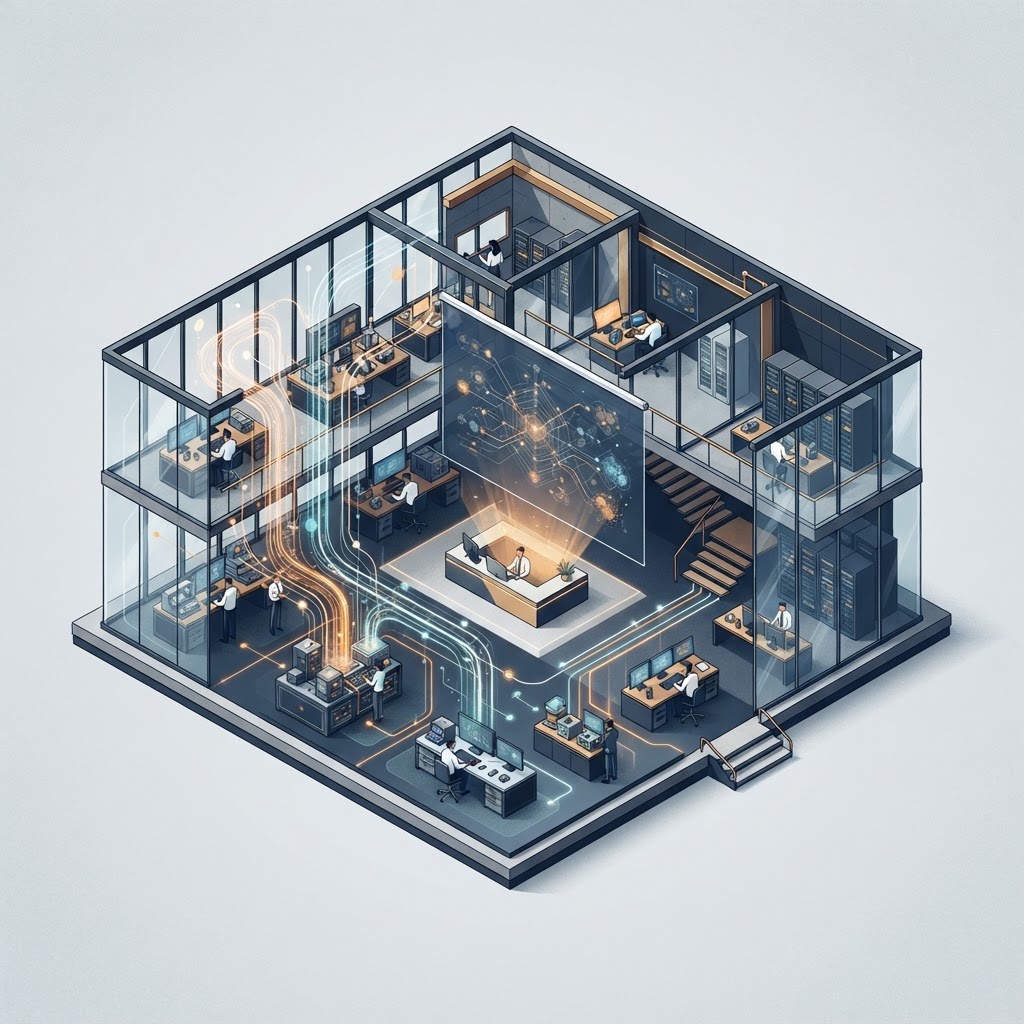
Industry self-regulation does not operate within a regulatory vacuum. Concurrently, regional authorities are accelerating scrutiny over algorithmic decision-making. Recent developments detailed in TLT's September 2026 AI Brief on UK and international policy emphasise that English common law now places explicit duties of care across application deployers and model providers alike.
While corporate consortia can harmonise red-team methodologies, national courts and statutory bodies will retain the authority to determine institutional liability. Consequently, technology practitioners cannot rely solely on vendor claims. Engineering teams must document internal testing processes to satisfy emerging public standards.
| Governance Layer | Primary Focus | Practical Enterprise Impact |
|---|---|---|
| Proposed Frontier Lab Consortium | Model capabilities, autonomous red-teaming, pre-release auditing | Standardised vendor ratings and safety tier certification |
| Statutory Jurisdictions (e.g. UK/EU) | Workplace monitoring, civil liability, automated decision rights | Mandatory risk assessments and legally binding accountability |
| Internal Enterprise Operations | Zero Trust Architecture, data telemetry, role-based tool limits | Continuous anomaly detection across live operational agents |
Practical Takeaway for Technology Careers
Enterprise AI readiness is shifting definitively from ad-hoc prompt crafting to verifiable systems governance. Professionals preparing for the next wave of adoption should align their skills with formalised evaluation frameworks.
Your immediate next step is to conduct an audit of the automated assistants currently connected to your team's code repositories or communications channels. Verify whether each tool operates under structured API rate controls, and document explicit rollback parameters for any agent possessing read-and-write permissions.